Compliance
Compliance-related changes
Monitoring And Analytics Features
New monitoring capabilities
Maintenance Features
Upkeep and reliability work
Compliance
SOC 2 / Type 1 Audit
Description Last month, we accomplished the following milestones:- Successfully completed the Soc2/Type1 Audit, including attestation. Detailed information is enclosed regarding the audit findings and outcomes.
- Commenced a 12-month Soc2/Type2 audit process, which will further evaluate and assess our compliance over an extended period.
Monitoring and Analytics Features
[End within], [Overlap] or [Start Within] in Date/Time range
Description The platform offers the ability to display metrics for Key Performance Indicators (KPIs) based on their duration. This includes options to filter metrics based on whether the KPI’s duration [ends within], [overlaps], or [starts within] a specified datetime range.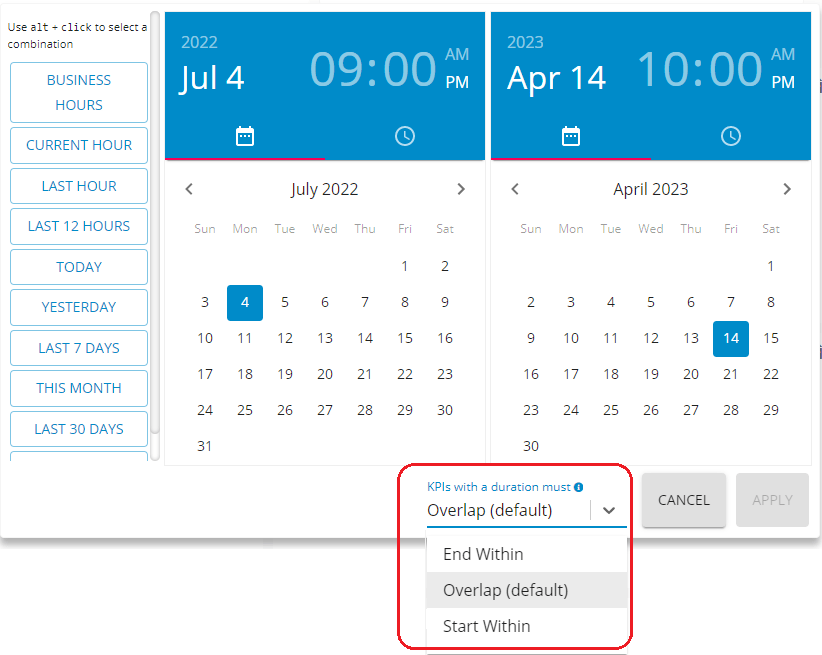
KPIs for Business, IT, Marketing, UX and Web Ops
Description The following are preconfigured Key Performance Indicators (KPIs) available in GermainUX:- KPIs/Pivots/Measures for Business Ops.
- KPIs/Pivots/Measures for IT Ops.
- KPIs/Pivots/Measures for Marketing Ops.
- KPIs/Pivots/Measures for UX Ops.
- KPIs/Pivots/Measures for Web Administrators.
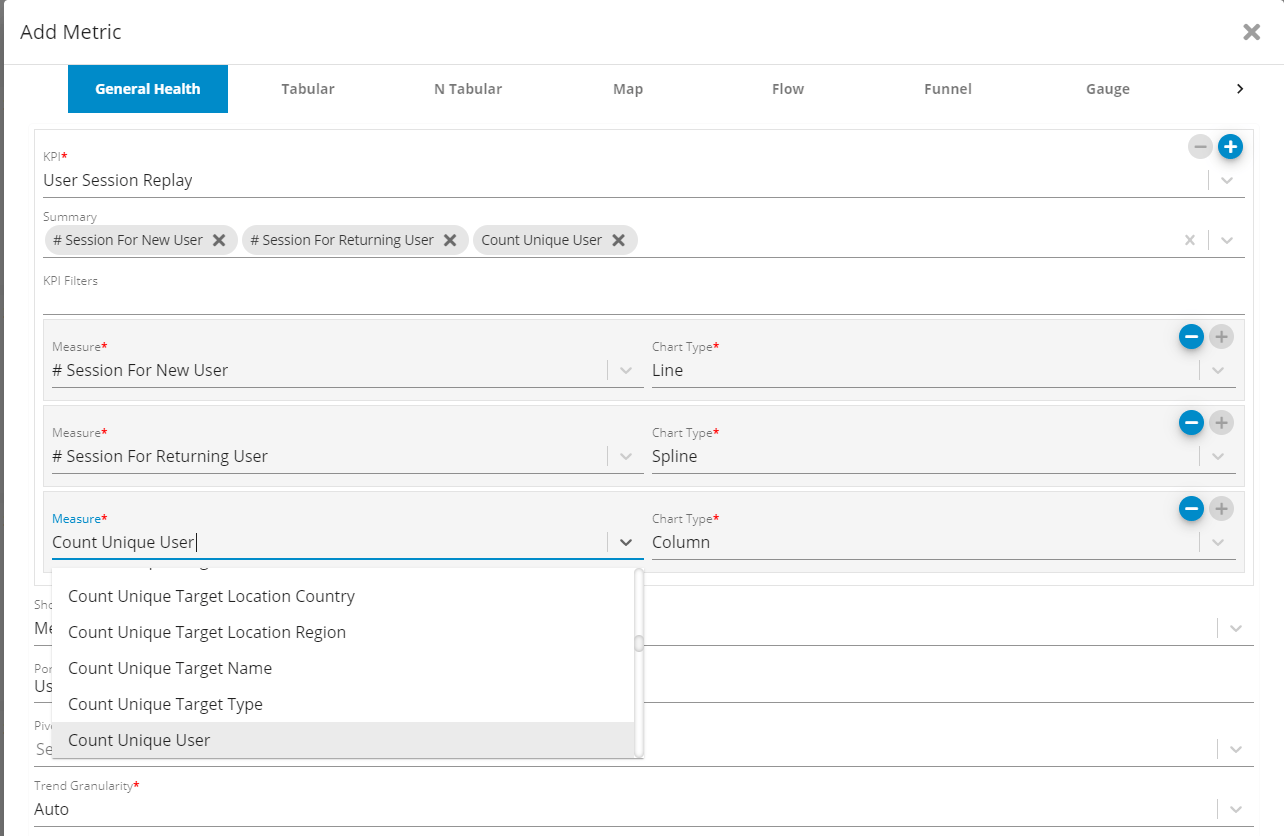
Measures for [User Session Replay] KPI
Description Several new measures have been added to the [User Session Replay] and [User Click] Key Performance Indicators (KPIs). The following are the new measures for the [User Session Replay] and [User Click] KPIs:- Count of New Users vs Returning users
- Top visited pages (volume per page)
- Mobile vs Desktop users (volume, performance)
- Top landing pages
- Top exit pages
- Top references
- Top campaigns
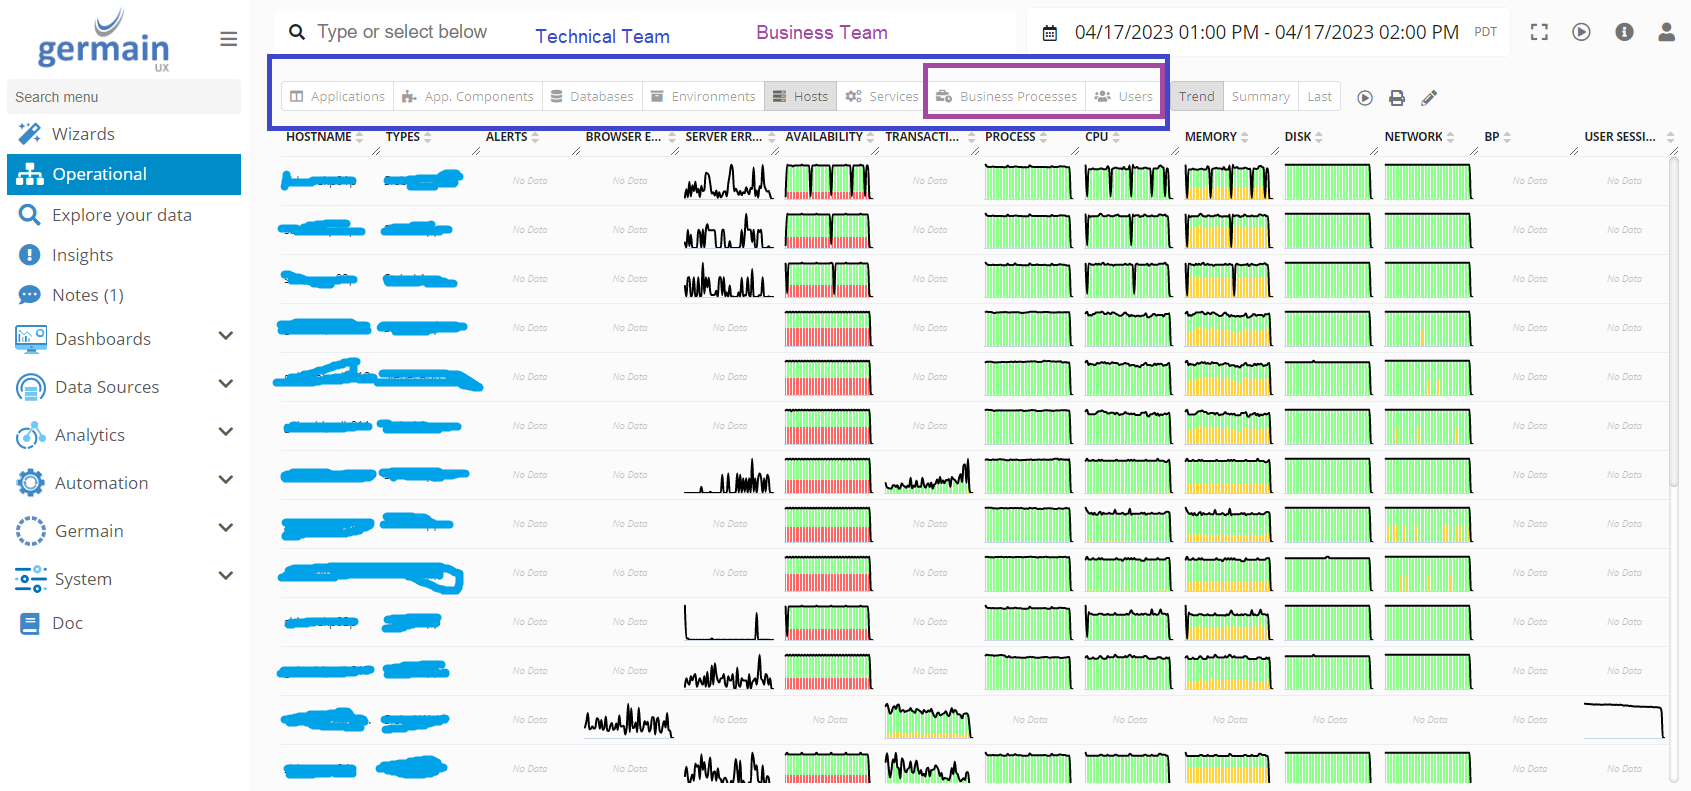
Operational Dashboard’s Tab Visibility
Description The visibility of tabs in the Operational Dashboard is determined by theTeam Type, either Business or Technical.- The Business Team has visibility to the following tabs: [Business Process] and [Users].
- The Technical Team has visibility to all tabs, including: [Application], [App Components], [Databases], [Environments], [Hosts], [Services], [Business Process], and [Users].
Render Blocking Status of a HTTP Request
Description Render-blocking resources refer to static files such as fonts, CSS, and JavaScript that can hinder or delay the browser from rendering page content promptly. The Render-blocking Status is now accessible through various Germain Key Performance Indicators (KPIs), such as the Outbound CSS Request KPI. More details about renderBlockingStatus: https://developer.mozilla.org/en-US/docs/Web/API/PerformanceResourceTiming/renderBlockingStatus Example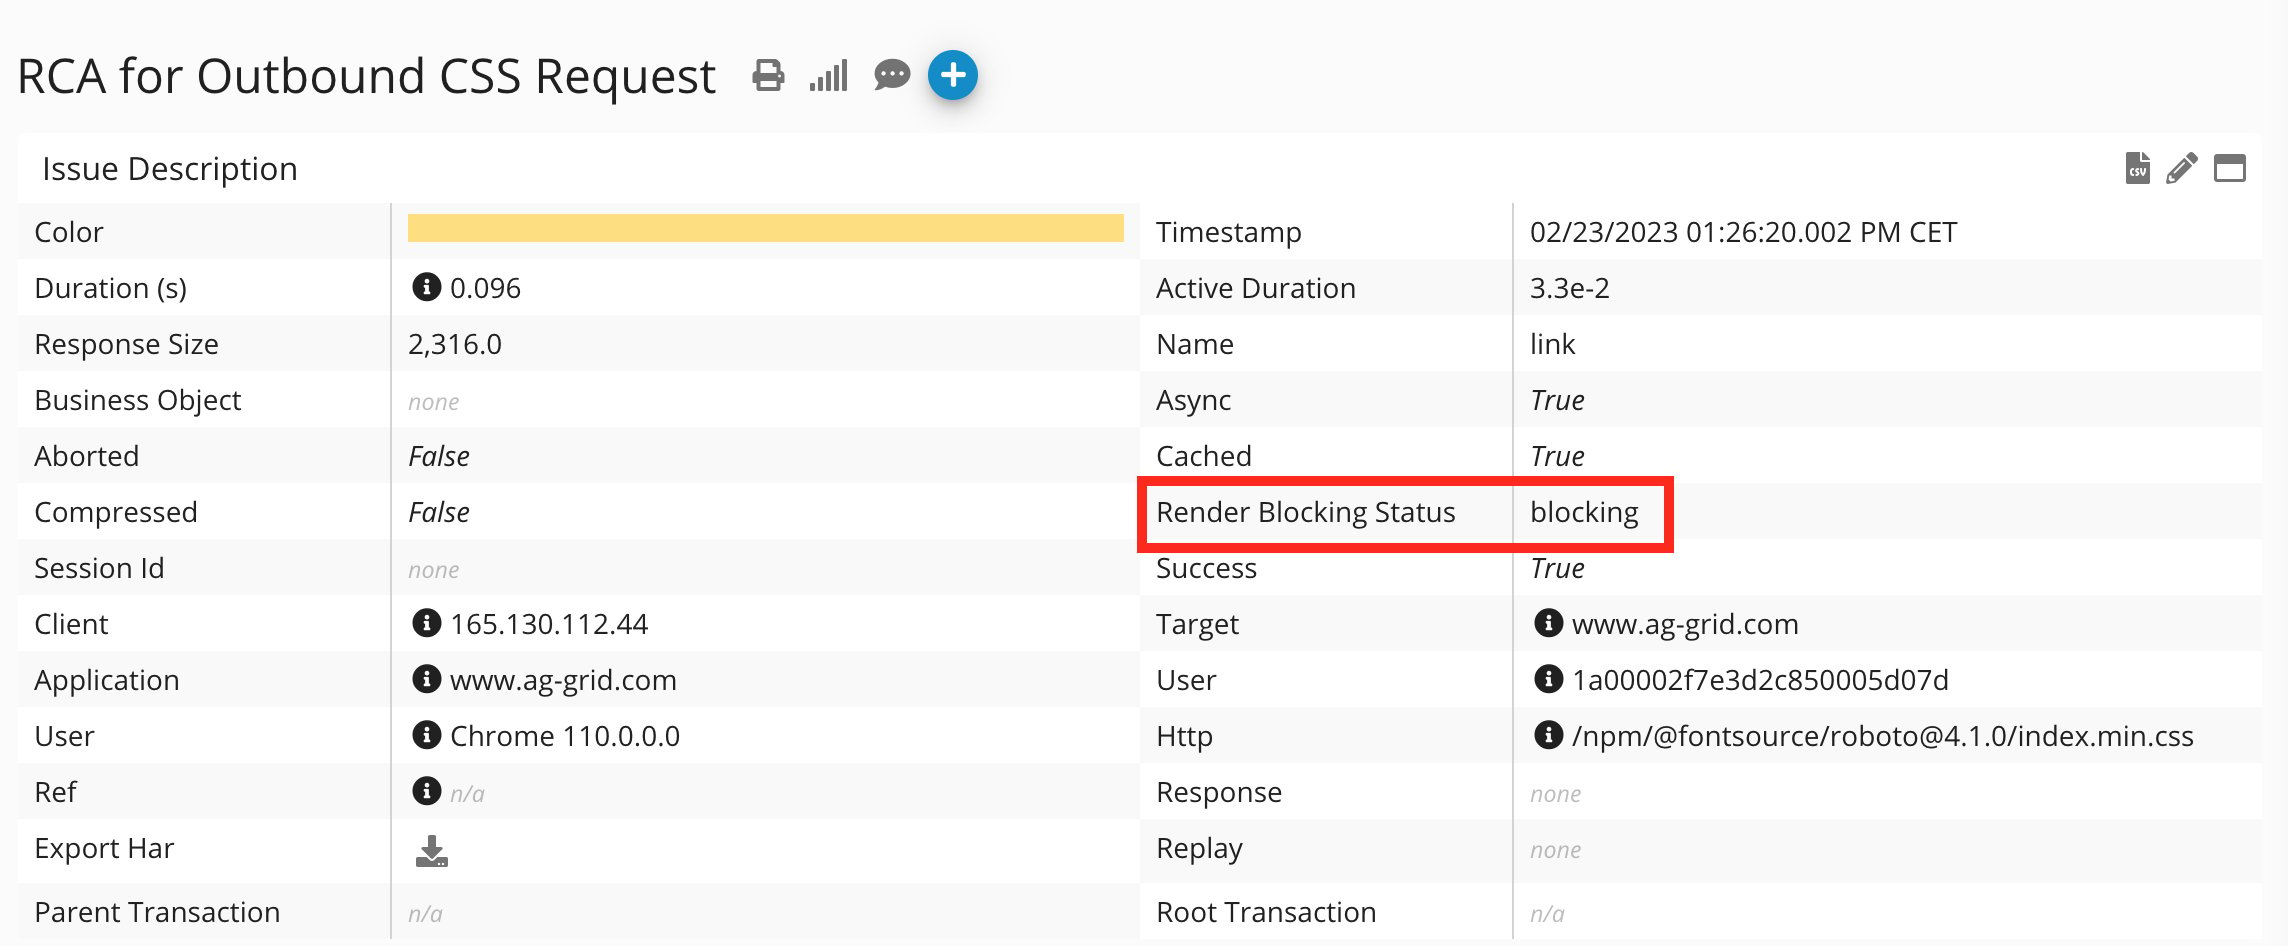
SALESFORCE.COM - More KPIs
Description Additional Key Performance Indicators (KPIs), portlets, and dashboards have been added to specifically monitor and provide insights on Salesforce performance.- GERMAIN UX KPIs FOR SALESFORCE.COM MONITORING AND INSIGHTS
- Salesforce Apex Class
- Salesforce Apex Code Coverage
- Salesforce Apex Custom Action
- Salesforce Apex Trigger
- Salesforce Api Event
Show all 43
Show all 43
- Salesforce Browser Performance Count
- Salesforce Bulk Api Result Event
- Salesforce Classic Record Event
- salesforce Code Debug Event
- Salesforce Code Exception
- salesforce Code Execution
- Salesforce Concurrent Long-running Apex Error Event
- Salesforce Credential Stuffing Event
- Salesforce Cron Job
- Salesforce External Service Custom Action
- Salesforce Flow Coverage
- Salesforce Flow Custom Action
- Salesforce Flow Interview
- Salesforce Health Check
- Salesforce Instance Status
- Salesforce Lightning List View Event
- Salesforce Lightning Record Event
- Salesforce Lightning User
- Salesforce List View
- Salesforce Log Generic Event
- Salesforce Login As Event
- Salesforce Login Event
- Salesforce Logout Event
- Salesforce Outbound HTTP Request
- Salesforce Page Performance Count
- Salesforce Platform Event Usage Metric
- Salesforce Process Approval
- Salesforce Process Rule
- Salesforce Record Change Event
- Salesforce Records Count
- Salesforce Report Anomaly Event
- Salesforce Report Execution Event
- Salesforce Resource Usage
- Salesforce Session Hijacking Event
- Salesforce Setup Audit
- Salesforce UI Switch
- Salesforce User Click
Maintenance Features
Data Security Dynamically Enforced at Team level
Description Data security is dynamically set the Team level depending on the type of “business data” that is being used/processed/accessed by the monitored users/on the monitored application. This is all customizable. Here’s how it works:- Each Team is assigned a unique accessId when it is created. These accessIds are visible on the Teams view. For example, the ‘Business Team’ may have accessId ‘t1’, while the ‘Development Team’ may have accessId ‘t2’.
- Data can be annotated with an expression that determines which teams have access to it. This is achieved by setting the ‘access’ field.
- For instance, a UxSession with access ‘t1 || t2’ would be visible to members of the Business Team (t1) or the Development Team (t2) who have access to view the data.
- If the access field is not set, anyone with permission to view data will be able to see the fact.
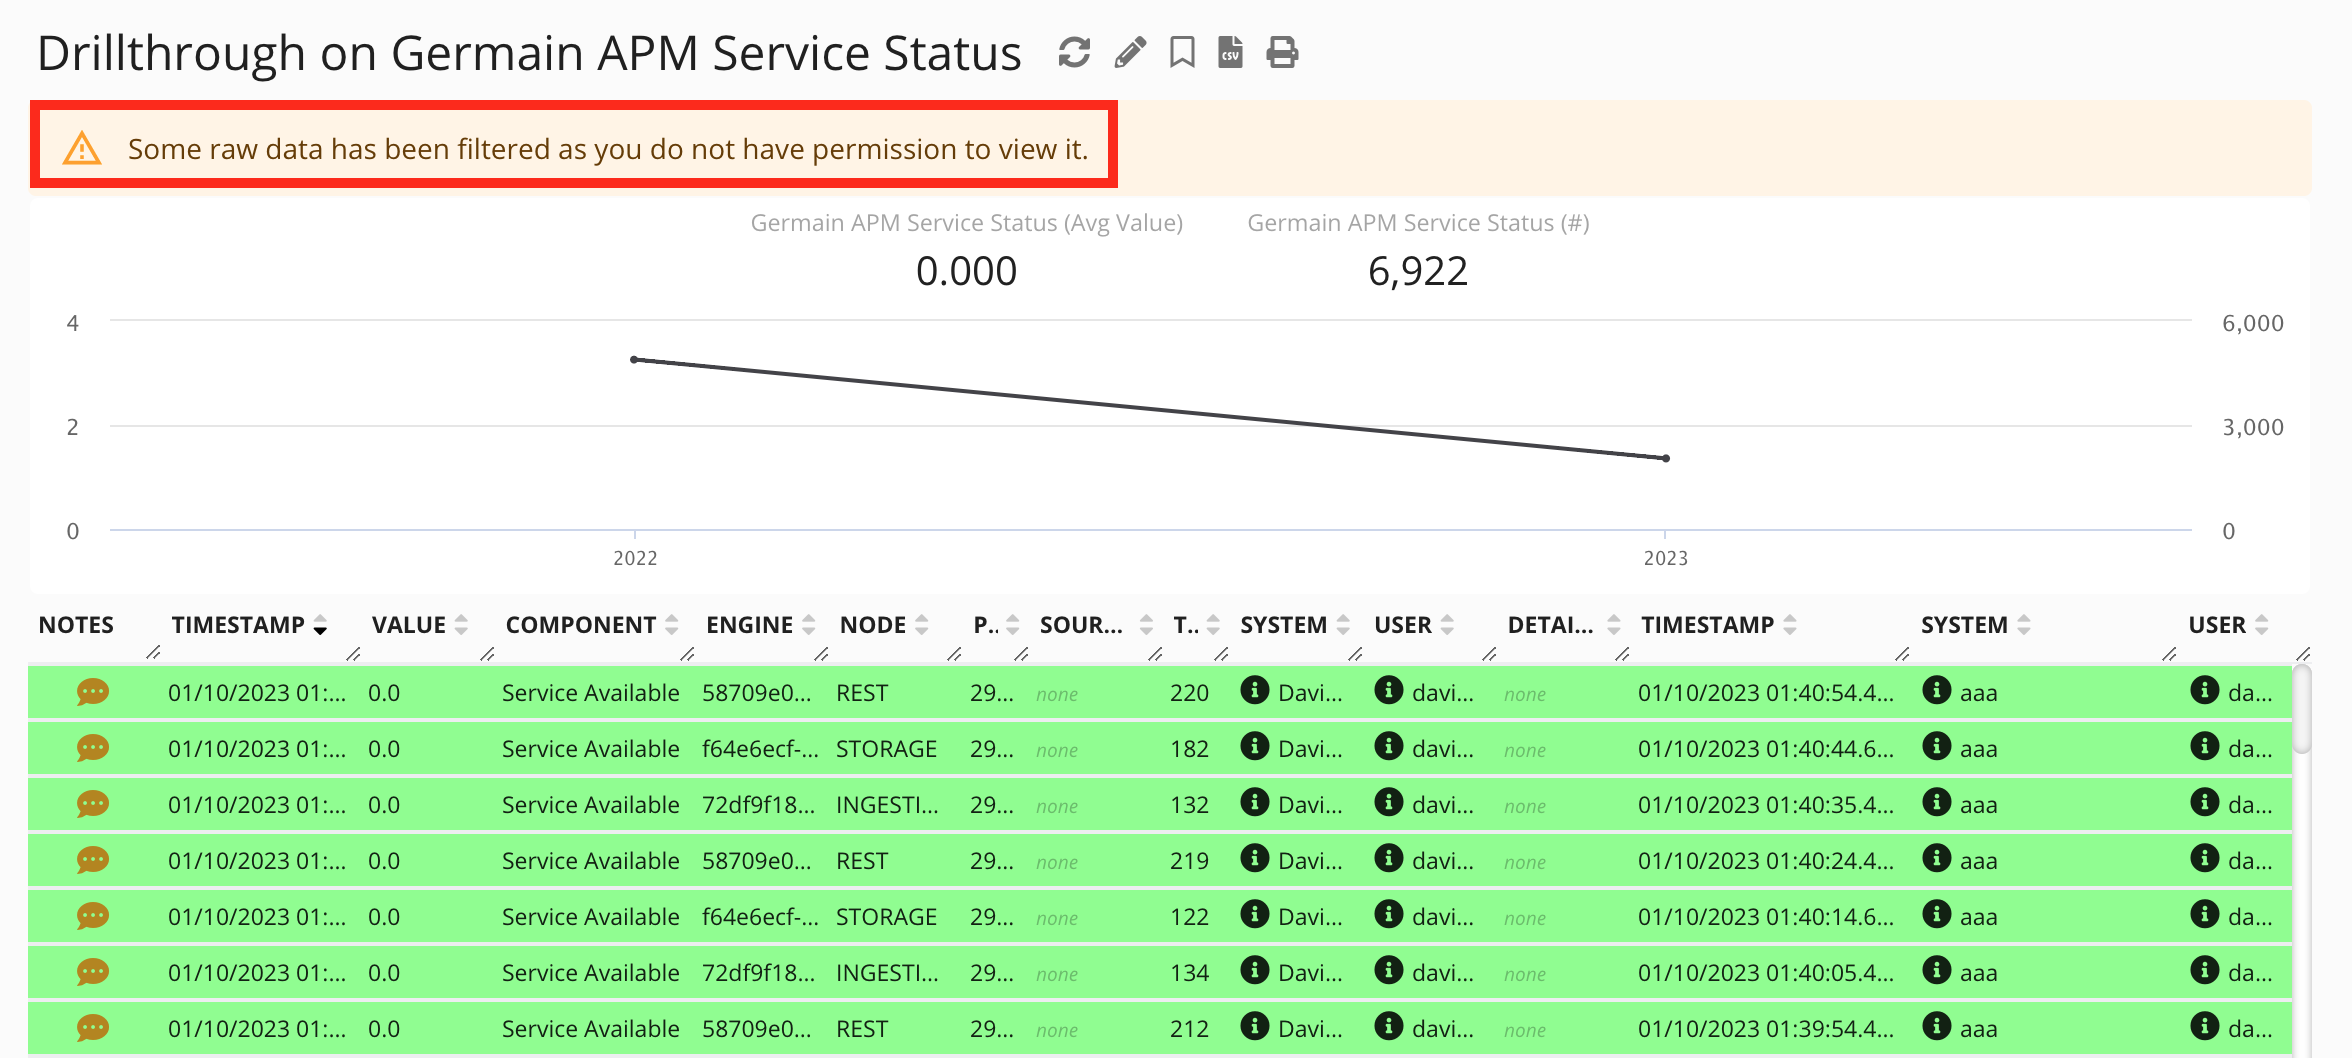
- When a user attempts to access an RCA (Root Cause Analysis) for a fact they don’t have access to, the data should not be visible to them. Similarly, the Drill-through feature and any RAW data exports should only display data that the user has access to.
OAuth - Custom Role Mapping
Description Germain now supports the execution of a custom function to extract Roles from an authenticated OAuth user, similar to how it supports LDAP. There are a few differences in Role Mapping between LDAP and OAuth:- In LDAP, only Groups and Roles are mapped. However, in OAuth, there are several entities that can be mapped to Roles, based on the OAuth provider and the requested scopes.
- Previously, when a user logged in via OAuth, they had to have the AuthenticationConfig.mapRolesFromDBUser configuration setting set to true and have a corresponding user in Germain DB. Alternatively, if AuthenticationConfig.createMissingDBUser was set to true, a DB user would be automatically created. These settings were necessary to obtain any roles because the default mapping from OAuth to GrantedAuthorities only considered the OAuth scopes.
Security and Vulnerabilities Fixes
All customers are required to update Germain with the below patches
Download
2022.3-61
2022.3-61
Standard:
https://germain-apm.s3.us-west-2.amazonaws.com/GermainAPM/2022/GermainAPMServer-2022.3-61-binary.tar.gz
https://germain-apm.s3.us-west-2.amazonaws.com/GermainAPM/2022/GermainAPMServer-2022.3-61-binary.zip
public.ecr.aws/h0m9e4y5/germainapm-engines:2022.3-61
public.ecr.aws/h0m9e4y5/germainapm-server:2022.3-61
public.ecr.aws/h0m9e4y5/germainapm-services:2022.3-61
GermainAPMEngine-2022.3-61-binary.tar.gz (no longer available) GermainAPMEngine-2022.3-61-binary.zip (no longer available) https://germain-apm.s3.us-west-2.amazonaws.com/GermainAPM/2022/GermainAPMServer-2022.3-61-binary.tar.gz
https://germain-apm.s3.us-west-2.amazonaws.com/GermainAPM/2022/GermainAPMServer-2022.3-61-binary.zip
GermainAPMService-2022.3-61-binary.tar.gz (no longer available) GermainAPMService-2022.3-61-binary.zip (no longer available)Docker: public.ecr.aws/h0m9e4y5/germainapm-engines:2022.3-61
public.ecr.aws/h0m9e4y5/germainapm-server:2022.3-61
public.ecr.aws/h0m9e4y5/germainapm-services:2022.3-61
2022.4-51
2022.4-51
Standard:
https://germain-apm.s3.us-west-2.amazonaws.com/GermainAPM/2022/GermainAPMServer-2022.4-51-binary.tar.gz
https://germain-apm.s3.us-west-2.amazonaws.com/GermainAPM/2022/GermainAPMServer-2022.4-51-binary.zip
public.ecr.aws/h0m9e4y5/germainapm-engines:2022.4-51
public.ecr.aws/h0m9e4y5/germainapm-server:2022.4-51
public.ecr.aws/h0m9e4y5/germainapm-services:2022.4-51
GermainAPMEngine-2022.4-51-binary.tar.gz (no longer available) GermainAPMEngine-2022.4-51-binary.zip (no longer available) https://germain-apm.s3.us-west-2.amazonaws.com/GermainAPM/2022/GermainAPMServer-2022.4-51-binary.tar.gz
https://germain-apm.s3.us-west-2.amazonaws.com/GermainAPM/2022/GermainAPMServer-2022.4-51-binary.zip
GermainAPMService-2022.4-51-binary.tar.gz (no longer available) GermainAPMService-2022.4-51-binary.zip (no longer available)Docker: public.ecr.aws/h0m9e4y5/germainapm-engines:2022.4-51
public.ecr.aws/h0m9e4y5/germainapm-server:2022.4-51
public.ecr.aws/h0m9e4y5/germainapm-services:2022.4-51
2022.5-48
2022.5-48
Standard:
public.ecr.aws/h0m9e4y5/germainapm-engines:2022.5-48
public.ecr.aws/h0m9e4y5/germainapm-server:2022.5-48
public.ecr.aws/h0m9e4y5/germainapm-services:2022.5-48
GermainAPMEngine-2022.5-48-binary.tar.gz (no longer available) GermainAPMEngine-2022.5-48-binary.zip (no longer available) GermainAPMServer-2022.5-48-binary.tar.gz (no longer available) GermainAPMServer-2022.5-48-binary.zip (no longer available) GermainAPMService-2022.5-48-binary.tar.gz (no longer available) GermainAPMService-2022.5-48-binary.zip (no longer available)Docker: public.ecr.aws/h0m9e4y5/germainapm-engines:2022.5-48
public.ecr.aws/h0m9e4y5/germainapm-server:2022.5-48
public.ecr.aws/h0m9e4y5/germainapm-services:2022.5-48
2023.1-14
2023.1-14
Standard:
public.ecr.aws/h0m9e4y5/germainapm-engines:2023.1-14
public.ecr.aws/h0m9e4y5/germainapm-server:2023.1-14
public.ecr.aws/h0m9e4y5/germainapm-services:2023.1-14
GermainAPMEngine-2023.1-14-binary.tar.gz (no longer available) GermainAPMEngine-2023.1-14-binary.zip (no longer available) GermainAPMServer-2023.1-14-binary.tar.gz (no longer available) GermainAPMServer-2023.1-14-binary.zip (no longer available) GermainAPMService-2023.1-14-binary.tar.gz (no longer available) GermainAPMService-2023.1-14-binary.zip (no longer available)Docker: public.ecr.aws/h0m9e4y5/germainapm-engines:2023.1-14
public.ecr.aws/h0m9e4y5/germainapm-server:2023.1-14
public.ecr.aws/h0m9e4y5/germainapm-services:2023.1-14
Get Help
Contact GermainUX Support
The Germain Team can help you set this up.
Can't find what you need?
Search all GermainUX docs with Ctrl + K, or use the feedback buttons at the bottom of this page to tell us what is missing.
The content of this document is proprietary to GERMAIN SOFTWARE.