Prerequisites
Details from Ping admins
Configure GermainUX
Adding the Ping connection
OAuth Provider Settings
Endpoint paths behind gateways
Troubleshooting
Diagnosing failed PingID logins
Integrate GermainUX with your organization’s Ping Identity environment to provide centralized authentication and single sign-on through OAuth 2.0 and OpenID Connect (OIDC).
Prerequisites
Before configuring the integration, obtain the following information from your Ping Identity administrator:Configure Ping Identity
Create an OAuth/OIDC client for GermainUX in your Ping Identity environment. Configure the client with the following settings:
The redirect URI registered with Ping Identity must exactly match the URI generated by GermainUX.
Record the client ID, client secret, endpoint URLs, and supported scopes before proceeding.
Configure GermainUX
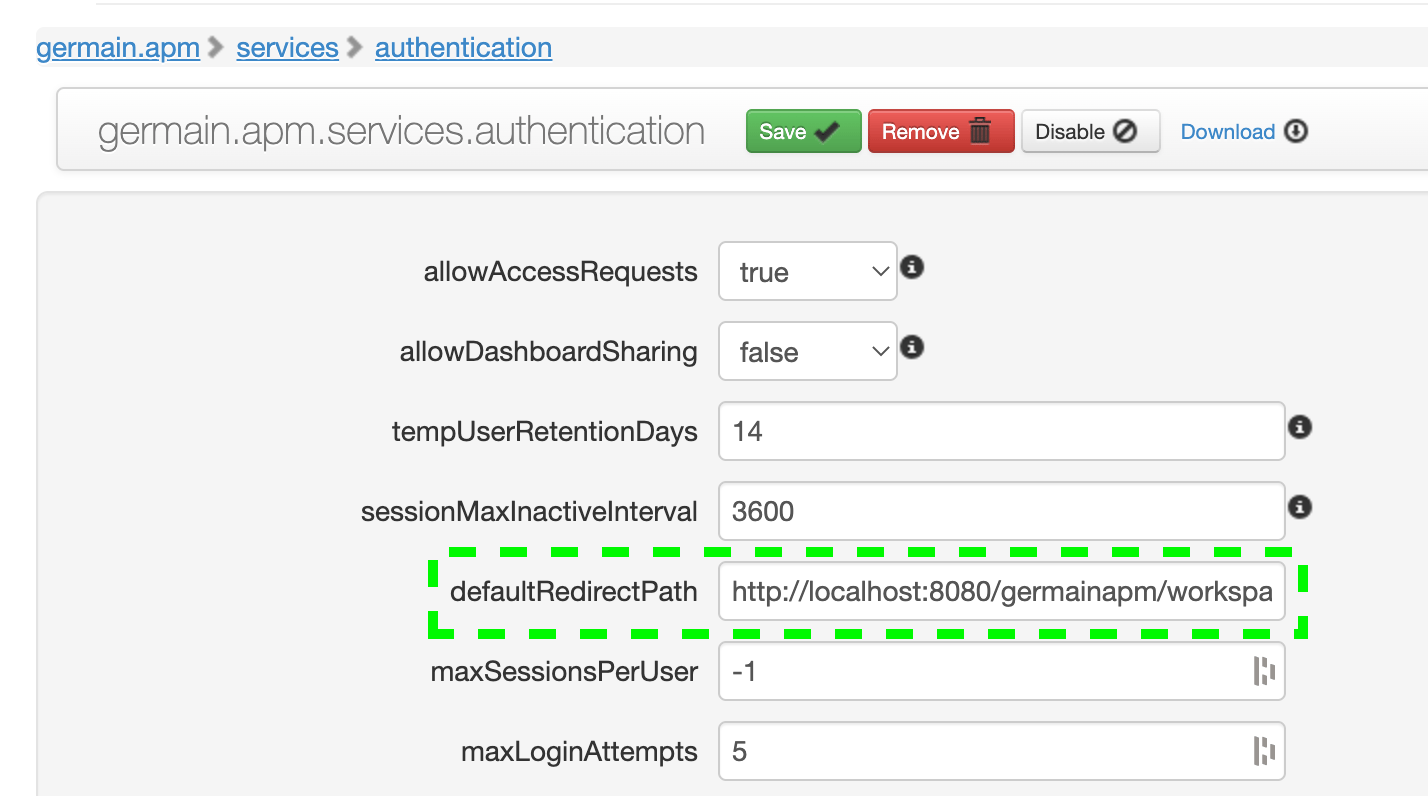
Set the Default Redirect Path
1
Sign in to GermainUX as an administrator
2
Go to System > System Settings > Root Config (Advanced)
3
Navigate to:
- In AuthenticationConfig, set Default Redirect Path to the GermainUX Workspace URL.
Add the OAuth Provider
1
Go to System > Auth Settings > Authentication
2
Click Add New Configuration
3
Select OAuth Provider
4
Click Next
5
Configure the provider using the settings below
6
Click Finish
7
Restart the Tomcat services to apply the configuration
OAuth Provider Settings
The endpoint paths can vary when PingFederate is deployed behind a gateway or under a custom context path such as
/fss. Confirm the URLs through your Ping Identity configuration or OpenID Provider metadata.
The standard PingFederate token endpoint is /as/token.oauth2, as documented in the official PingFederate token endpoint reference.
Public OAuth Clients and PKCE
A confidential OAuth client using a client secret is recommended for GermainUX server-side authentication. If your organization requires a public OAuth client:Validate the Integration
After restarting Tomcat:1
Open the GermainUX login page
2
Confirm that Login with PingID appears as an authentication option
3
Select the PingID option
4
Authenticate through your organization’s Ping Identity service
5
Confirm that you are redirected to the GermainUX Workspace
6
Verify that the correct GermainUX user and permissions are applied
Troubleshooting
If authentication fails, verify the following:
For additional diagnostic information, enable
DEBUG logging in the REST service for:
Get Help
Contact GermainUX Support
The GermainUX team helps you get up and running faster, empower your team, turn data into actionable insights, and optimize performance to deliver measurable business outcomes.
Can't find what you need?
Search all GermainUX docs with Ctrl + K, or use the feedback buttons at the bottom of this page to tell us what is missing.
The content of this document is proprietary to GERMAIN SOFTWARE.