GermainUX can authenticate Workspace users through an LDAP directory and map their LDAP group memberships to GermainUX Roles.
LDAP integration overview
Benefits of LDAP integration
LDAP Provider Settings
Directory connection options
Configure Role Mapping
Map LDAP groups to roles
Validate the Configuration
Test with a standard account
LDAP integration overview
LDAP integration allows organizations to:- Manage users centrally in an existing directory
- Authenticate users with their directory credentials
- Map LDAP groups to GermainUX Roles
- Apply GermainUX permissions without creating separate passwords
- Revoke Workspace access through the directory
Before You Begin
Obtain the following information from your LDAP administrator:- LDAP server URL
- Service-account distinguished name and password
- User and group search bases
- User and group search filters
- Group attribute containing the GermainUX Role name
Configure LDAP Authentication
- Log in to the Germain Workspace as an administrator.
- Go to System > Auth Settings > Authentication.
- Click Add New Configuration.
- Select LDAP Provider.
- Click Next.
- Configure the LDAP provider fields.
- Click Finish.
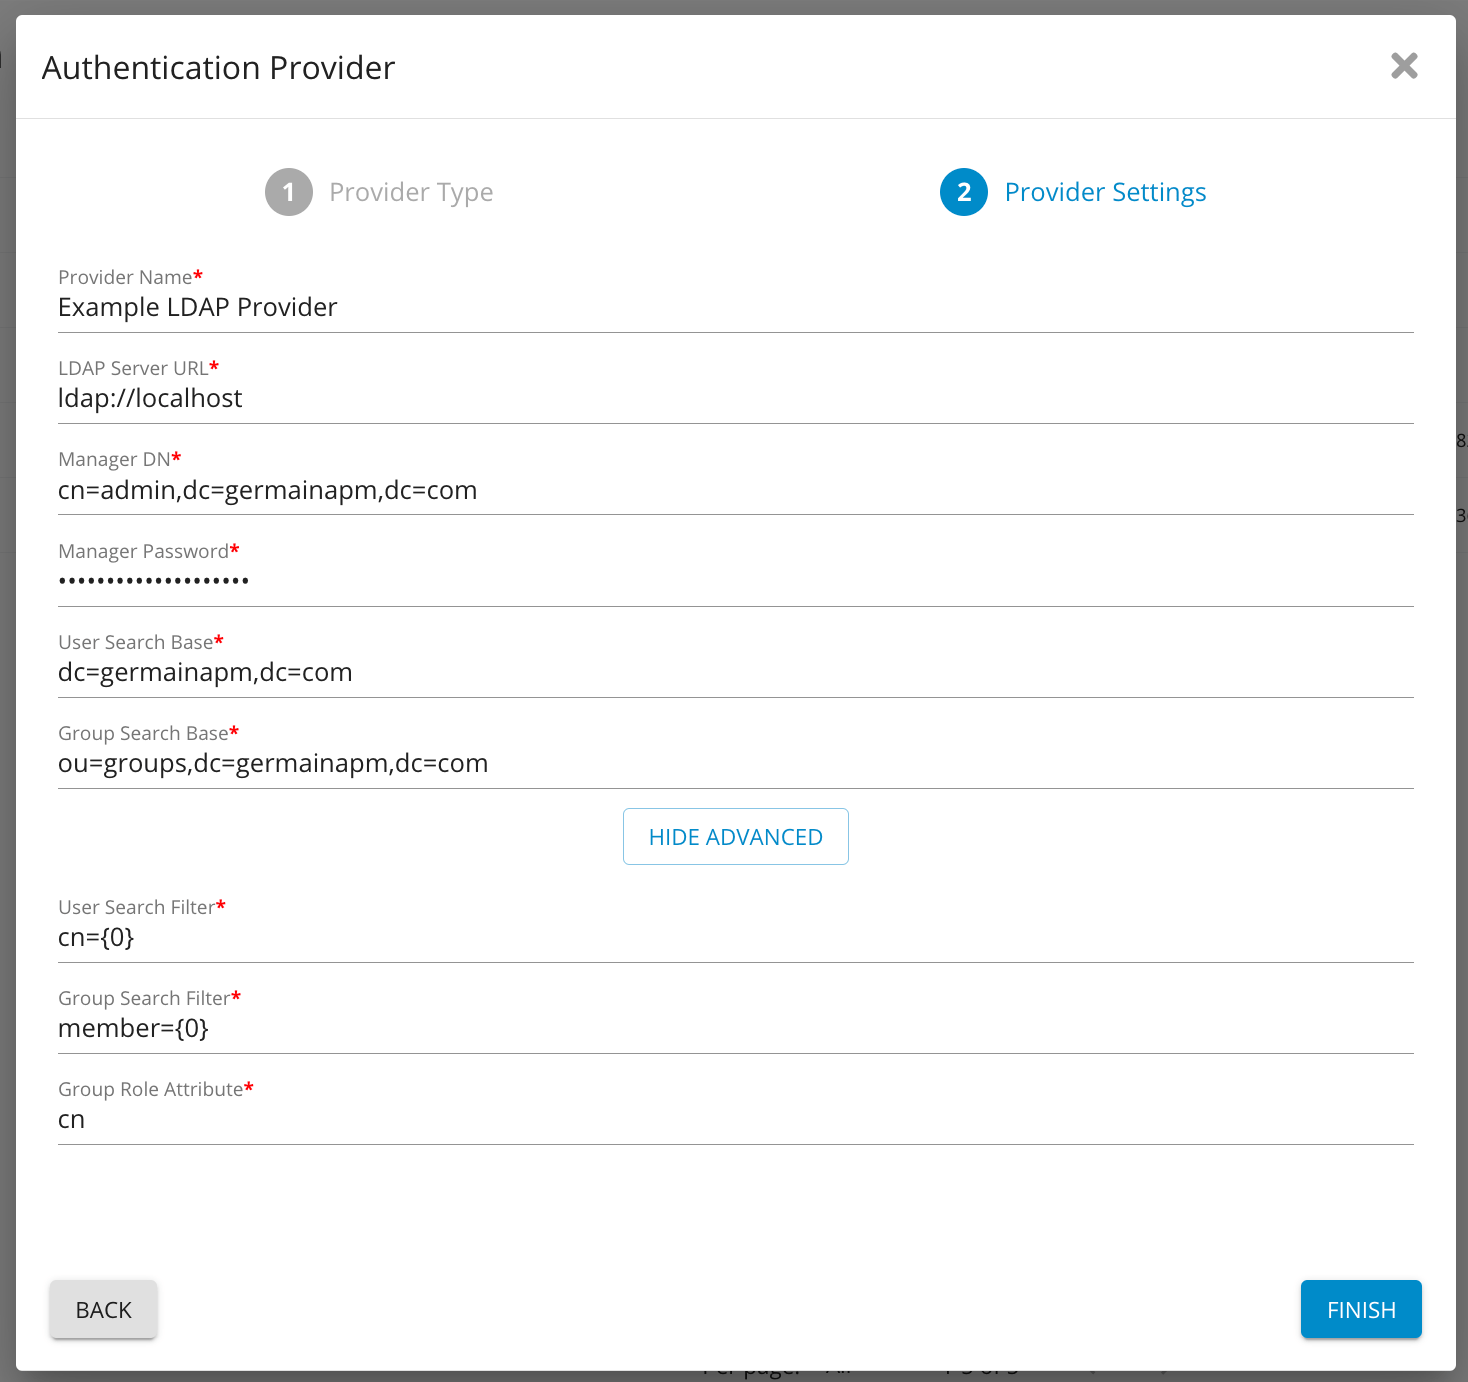
LDAP Provider Settings
Search-Filter Examples
User Search Filter
{0} represents the username entered on the GermainUX login page. This example searches for a user whose cn attribute matches that username.
Another commonly used filter is:
Group Search Filter
member attribute contains the authenticated user’s distinguished name.
The exact filter depends on the directory structure and LDAP implementation used by your organization.
Configure Role Mapping
GermainUX uses the value returned by Group Role Attribute to map LDAP groups to GermainUX Roles. For example, if an LDAP group has:- LDAP group names match the corresponding GermainUX Role names
- Each Role has the appropriate permissions
- Users belong to the required LDAP groups
- Role names use consistent capitalization and spelling
Manage LDAP Users
Create, update, disable, and remove users through your LDAP directory. To grant a user GermainUX access:1
Create or identify the user in LDAP
2
Add the user to the appropriate LDAP group
3
Ensure that a matching Role exists in GermainUX
4
Ask the user to log in with their LDAP credentials
Log In
1
Open the GermainUX login page
2
Enter the LDAP username and password
3
GermainUX authenticates the credentials against LDAP
4
GermainUX retrieves the user’s group memberships
5
Matching GermainUX Roles determine the user’s permissions
6
After successful authentication, the Germain Workspace opens
Validate the Configuration
Test the integration with a non-administrator LDAP account. Confirm that:- Valid LDAP credentials allow the user to log in
- Invalid credentials are rejected
- LDAP groups map to the expected GermainUX Roles
- The user can access only the authorized features
- Removing the user from a mapped group removes the corresponding permissions
Get Help
Contact GermainUX Support
The GermainUX team helps you get up and running faster, empower your team, turn data into actionable insights, and optimize performance to deliver measurable business outcomes.
Can't find what you need?
Search all GermainUX docs with Ctrl + K, or use the feedback buttons at the bottom of this page to tell us what is missing.
The content of this document is proprietary to GERMAIN SOFTWARE.