Integrate GermainUX Alerts with Moogsoft
Create a Custom Integration in Moogsoft
Recommended Event Fields
Security and Operational Considerations
Integrate GermainUX Alerts with Moogsoft
GermainUX can send real-time alerts and events to Moogsoft APEX AIOps Incident Management through an HTTP Action. The integration helps operations teams detect, correlate, prioritize, and resolve issues by sending GermainUX SLA violations and other monitored conditions directly to Moogsoft.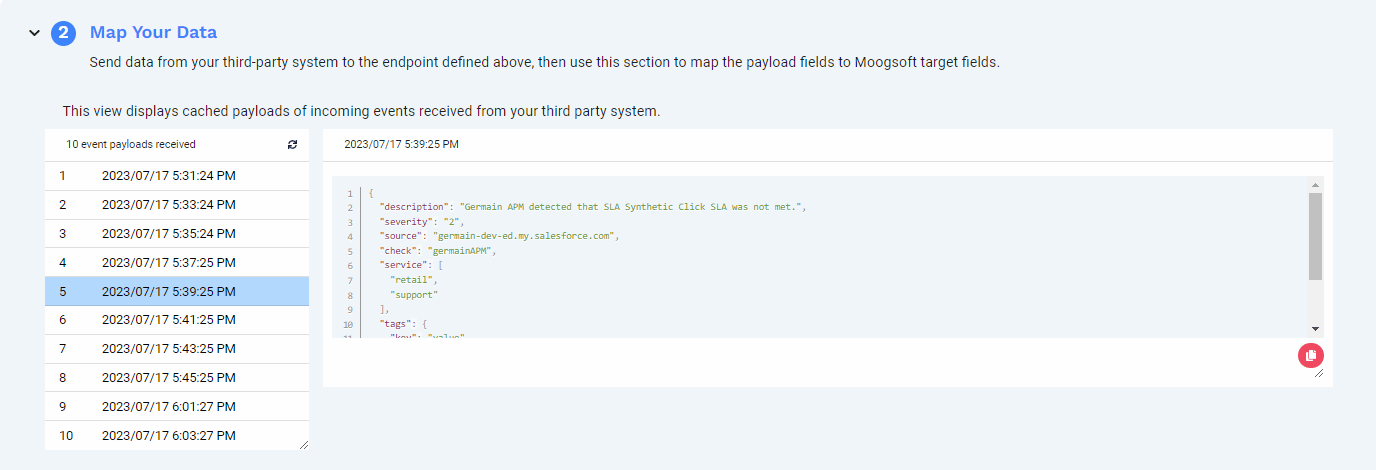
- When an SLA is breached
- When a synthetic scenario fails
- When a critical error or anomaly is detected
- On a configured schedule
- Through a manual execution
Create a Custom Integration in Moogsoft
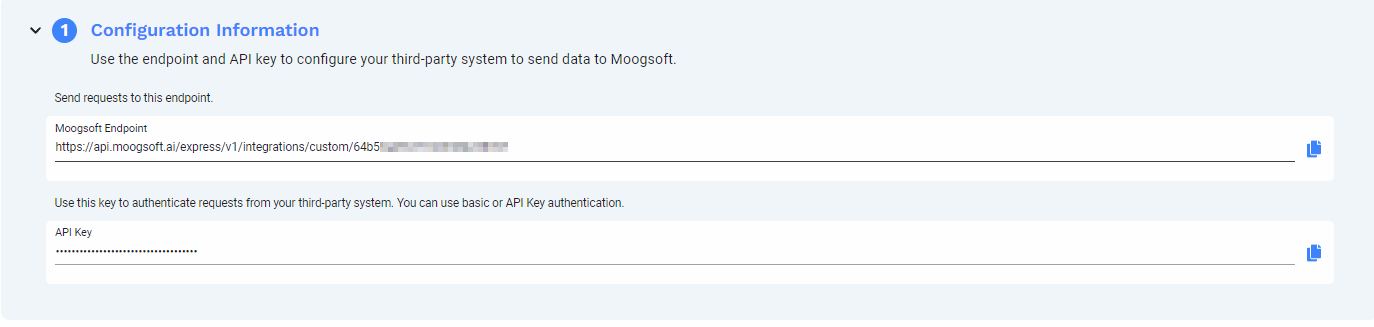
Sign in to Moogsoft APEX AIOps Incident Management
Go to Integrations > Inbound Integrations > Create Your Own Integration
Select Add New Integration
Enter a unique integration name and optional description
Select Events as the data type
Save the integration
Copy the generated endpoint and obtain an API key
Configure the required event-field mappings and severity mappings
Validate and enable the integration
Create the GermainUX HTTP Action
Go to: GermainUX Workspace > Automation > HTTP Select the Add icon to open the HTTP Action wizard.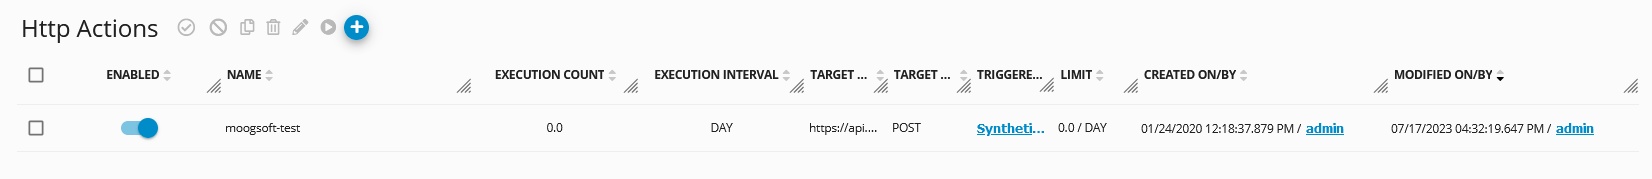
1 Step 1: Configure the Action
Enter the action settings:2 Step 2: Configure the HTTP Request
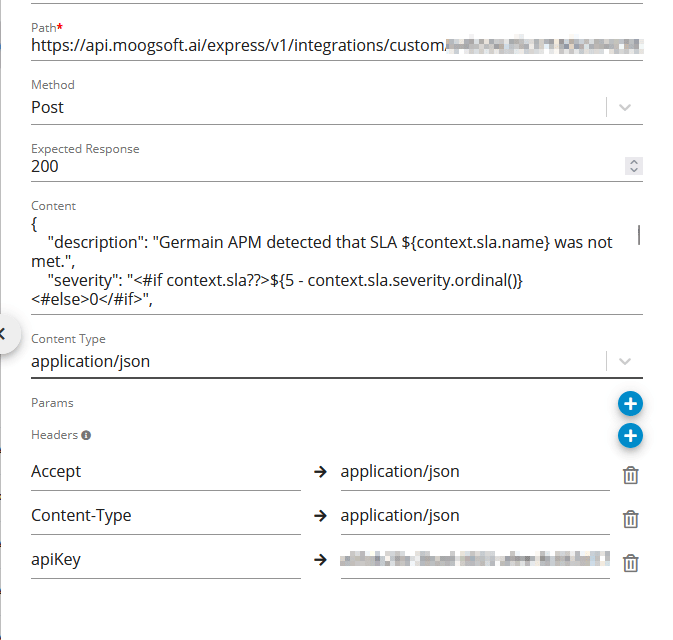
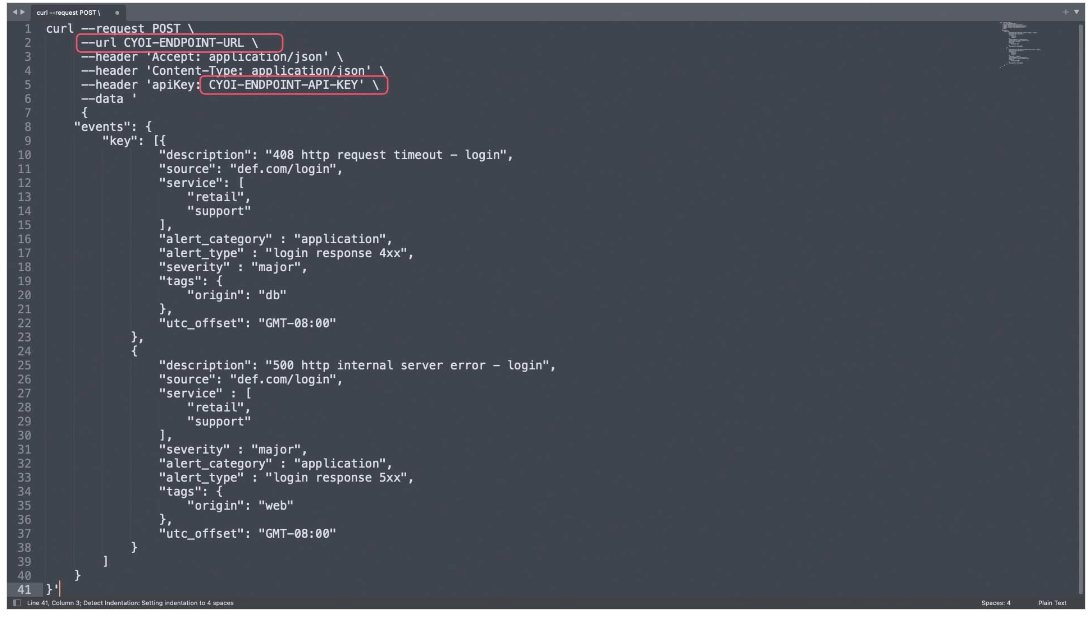
Example Request Body
Example Headers
3 Step 3: Assign the Trigger
Configure when GermainUX should send the event. For example, to create a Moogsoft event when a synthetic scenario fails:Select the synthetic-scenario KPI
Configure or select its failure SLA
Add the Moogsoft HTTP Action as the SLA Action
Save the SLA and action configuration
4 Step 4: Finish and Test
Complete the wizard
Run the HTTP Action manually
Confirm that GermainUX receives a successful HTTP response
Open the Moogsoft custom integration
Confirm that the test payload appears in Map Your Data
Map the incoming fields to the appropriate Moogsoft event fields
Validate and enable the integration
Force a controlled GermainUX SLA breach and confirm that a new Moogsoft event is created
Recommended Event Fields
Security and Operational Considerations
- Store the Moogsoft API key as a protected credential.
- Restrict access to users authorized to modify the HTTP Action.
- Use HTTPS only.
- Avoid sending unnecessary personal or sensitive data.
- Configure retries and execution limits carefully.
- Prevent duplicate incidents through Moogsoft deduplication and GermainUX Quiet Time.
- Test severity mappings before production use.
- Monitor failed HTTP executions and API-key expiration.
Get Help
Contact GermainUX Support
Can't find what you need?
The content of this document is proprietary to GERMAIN SOFTWARE LLC.